Audit log
Audit log. The API writes one row for every mutation that passes through /v1/admin, taking the actor from the x-admin-actor / x-admin-actor-email headers the dashboard sets from the session. Nothing done through the public API with an API key appears here — that is your backend's job to log.
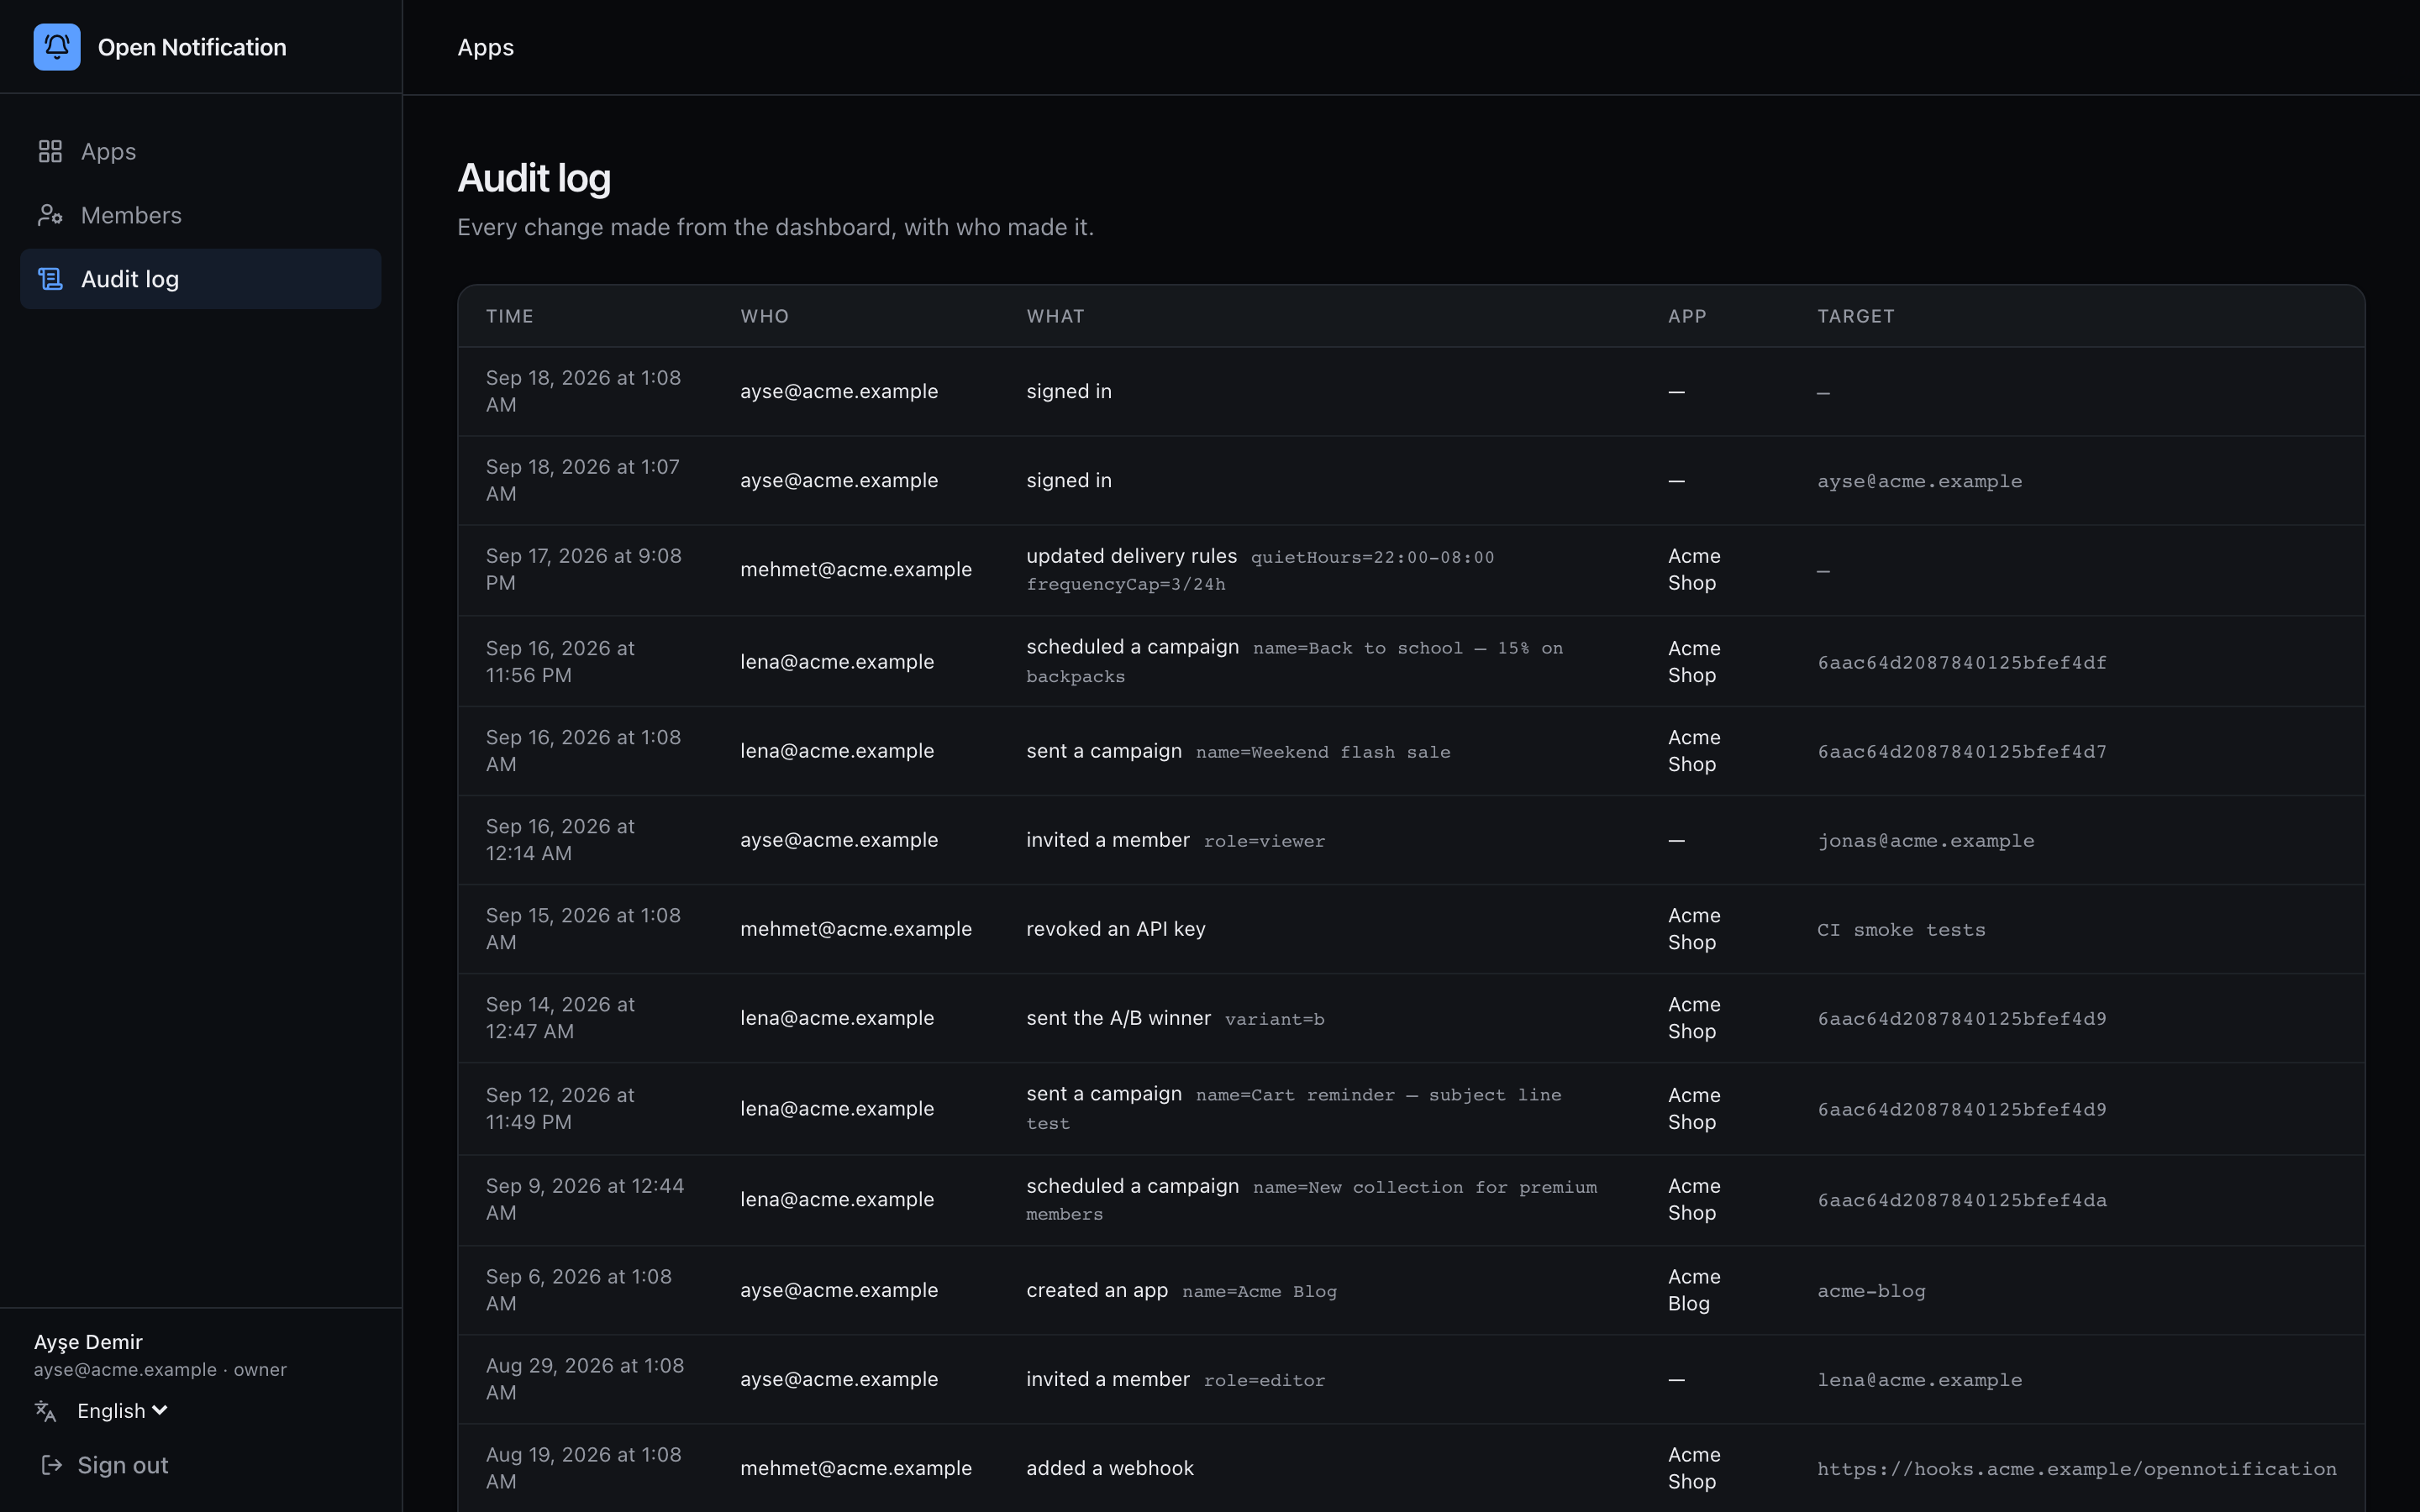
Columns: time, actor (name and e-mail), action in plain words, app, target, details. Filter by app with the App selector. Newest first, cursor-paged.
Actions recorded
| Action | Plain-words label | Target |
|---|---|---|
app.create | created an app | slug |
credentials.apns / fcm / webpush | updated a credential | bundle id / project id / subject |
key.create / key.revoke | generated / revoked an API key | key label |
delivery.update | changed delivery rules | — |
webhook.create / webhook.delete / rotate / enable | webhook changes | URL |
campaign.send / campaign.schedule / campaign.cancel | sent / scheduled / cancelled a campaign | campaign id (name in details) |
campaign.test_send | sent a test | external id, recipients |
campaign.send_winner | sent the A/B winner | variant, follow-up campaign id |
member.invite / reinvite / update / remove | member changes | |
auth.login / auth.accept_invite / auth.change_password | account events |
Entries are kept indefinitely. The collection is audit in Mongo if you want to ship it elsewhere.